

Video guide: Inviting your team
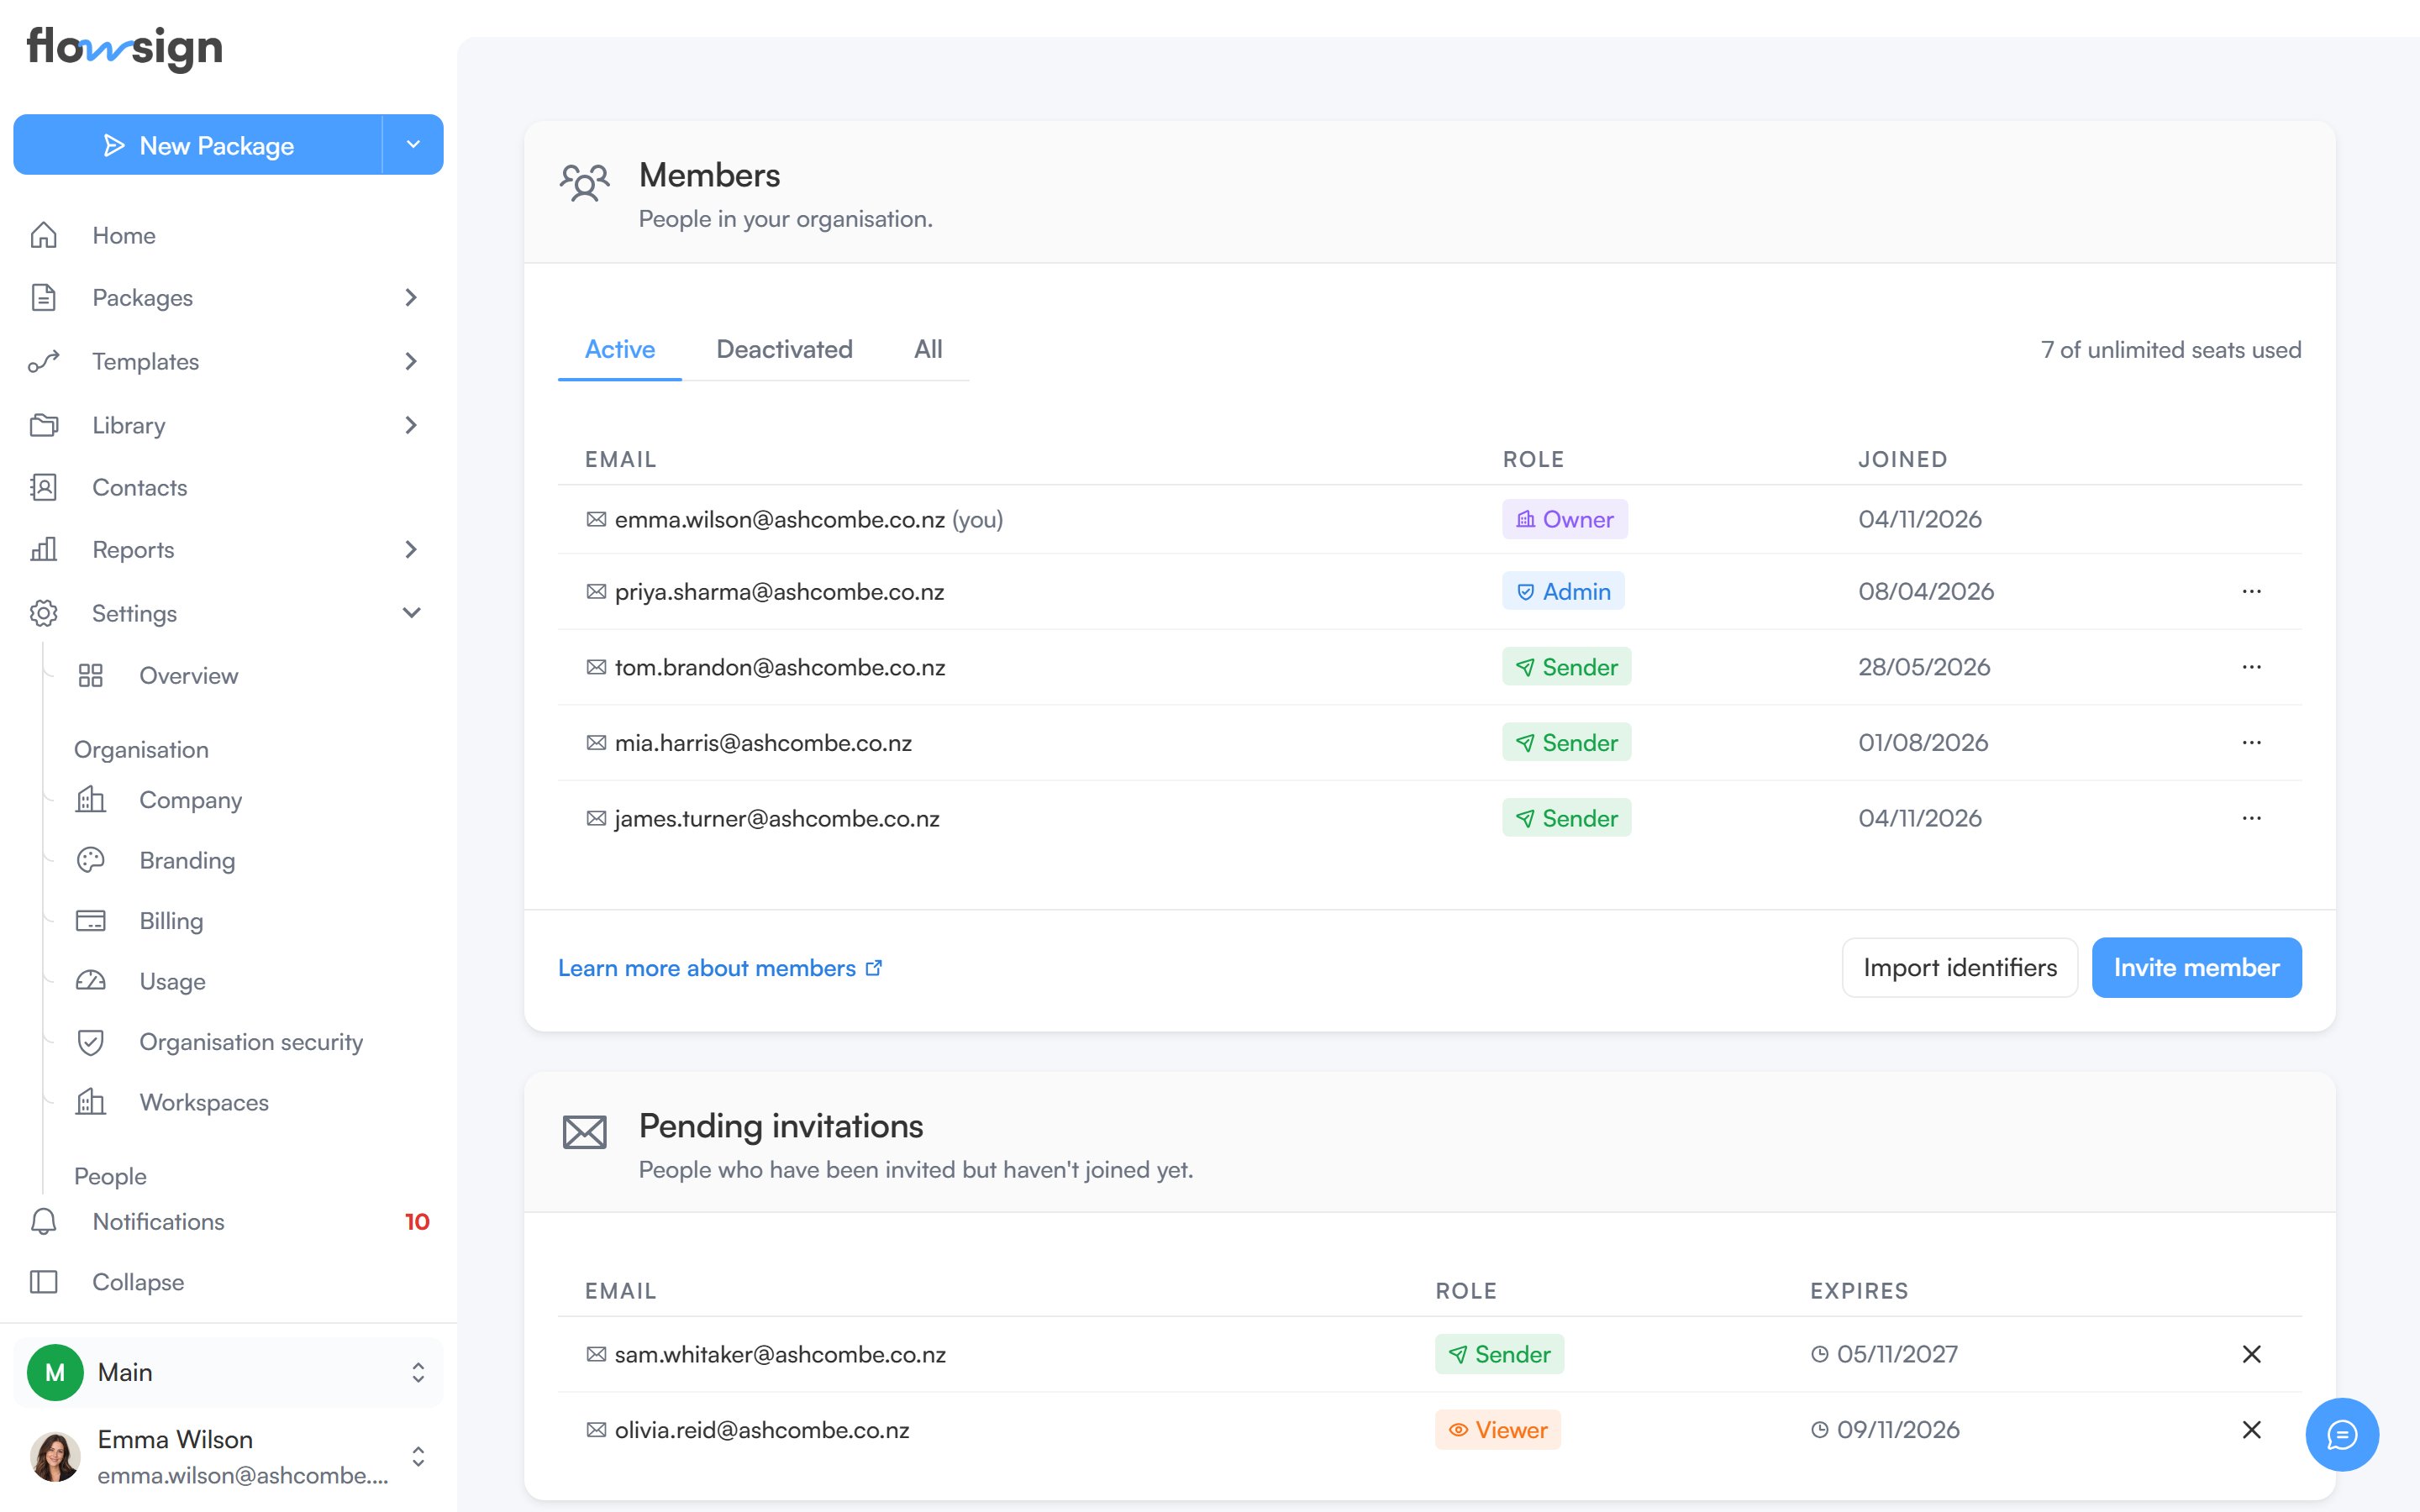
The members table, with each person's role.
Members
Anyone with permission to view members can open this page. A seat count sits above the table, for example “4 of 10 seats used”. Invite member sits below the table, beside Import identifiers. Inviting needs the Invite members permission. Owners hold it, and a custom role can be given it as one of its high-risk powers (see Roles & Permissions). Someone who isn’t an Owner invites people into their own workspace, with a role that has less access than their own. Invite member opens a dialog to set an Email address and a Permission profile, plus a Workspace when you can invite into more than one. If the email belongs to someone already in your organisation, the dialog says so and they’re added to the chosen workspace straight away, with no invitation to accept. They are told in the app and by email, and can switch that off under You’re added to a workspace in their notification preferences. Invite member is disabled at your plan’s seat limit.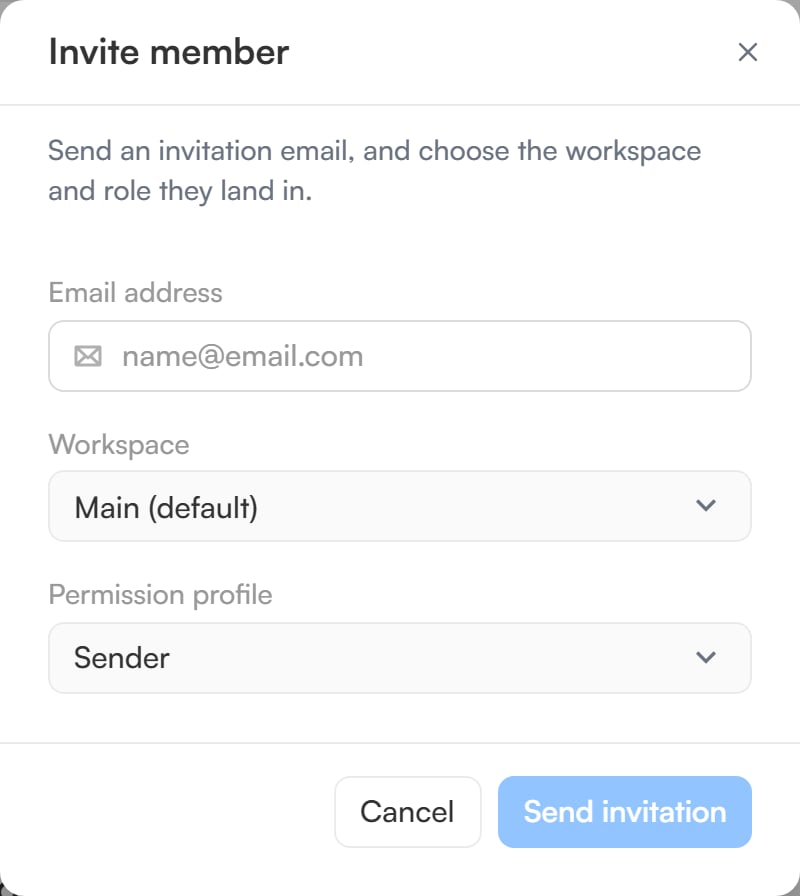
The Invite member dialog, setting an email address and permission profile.
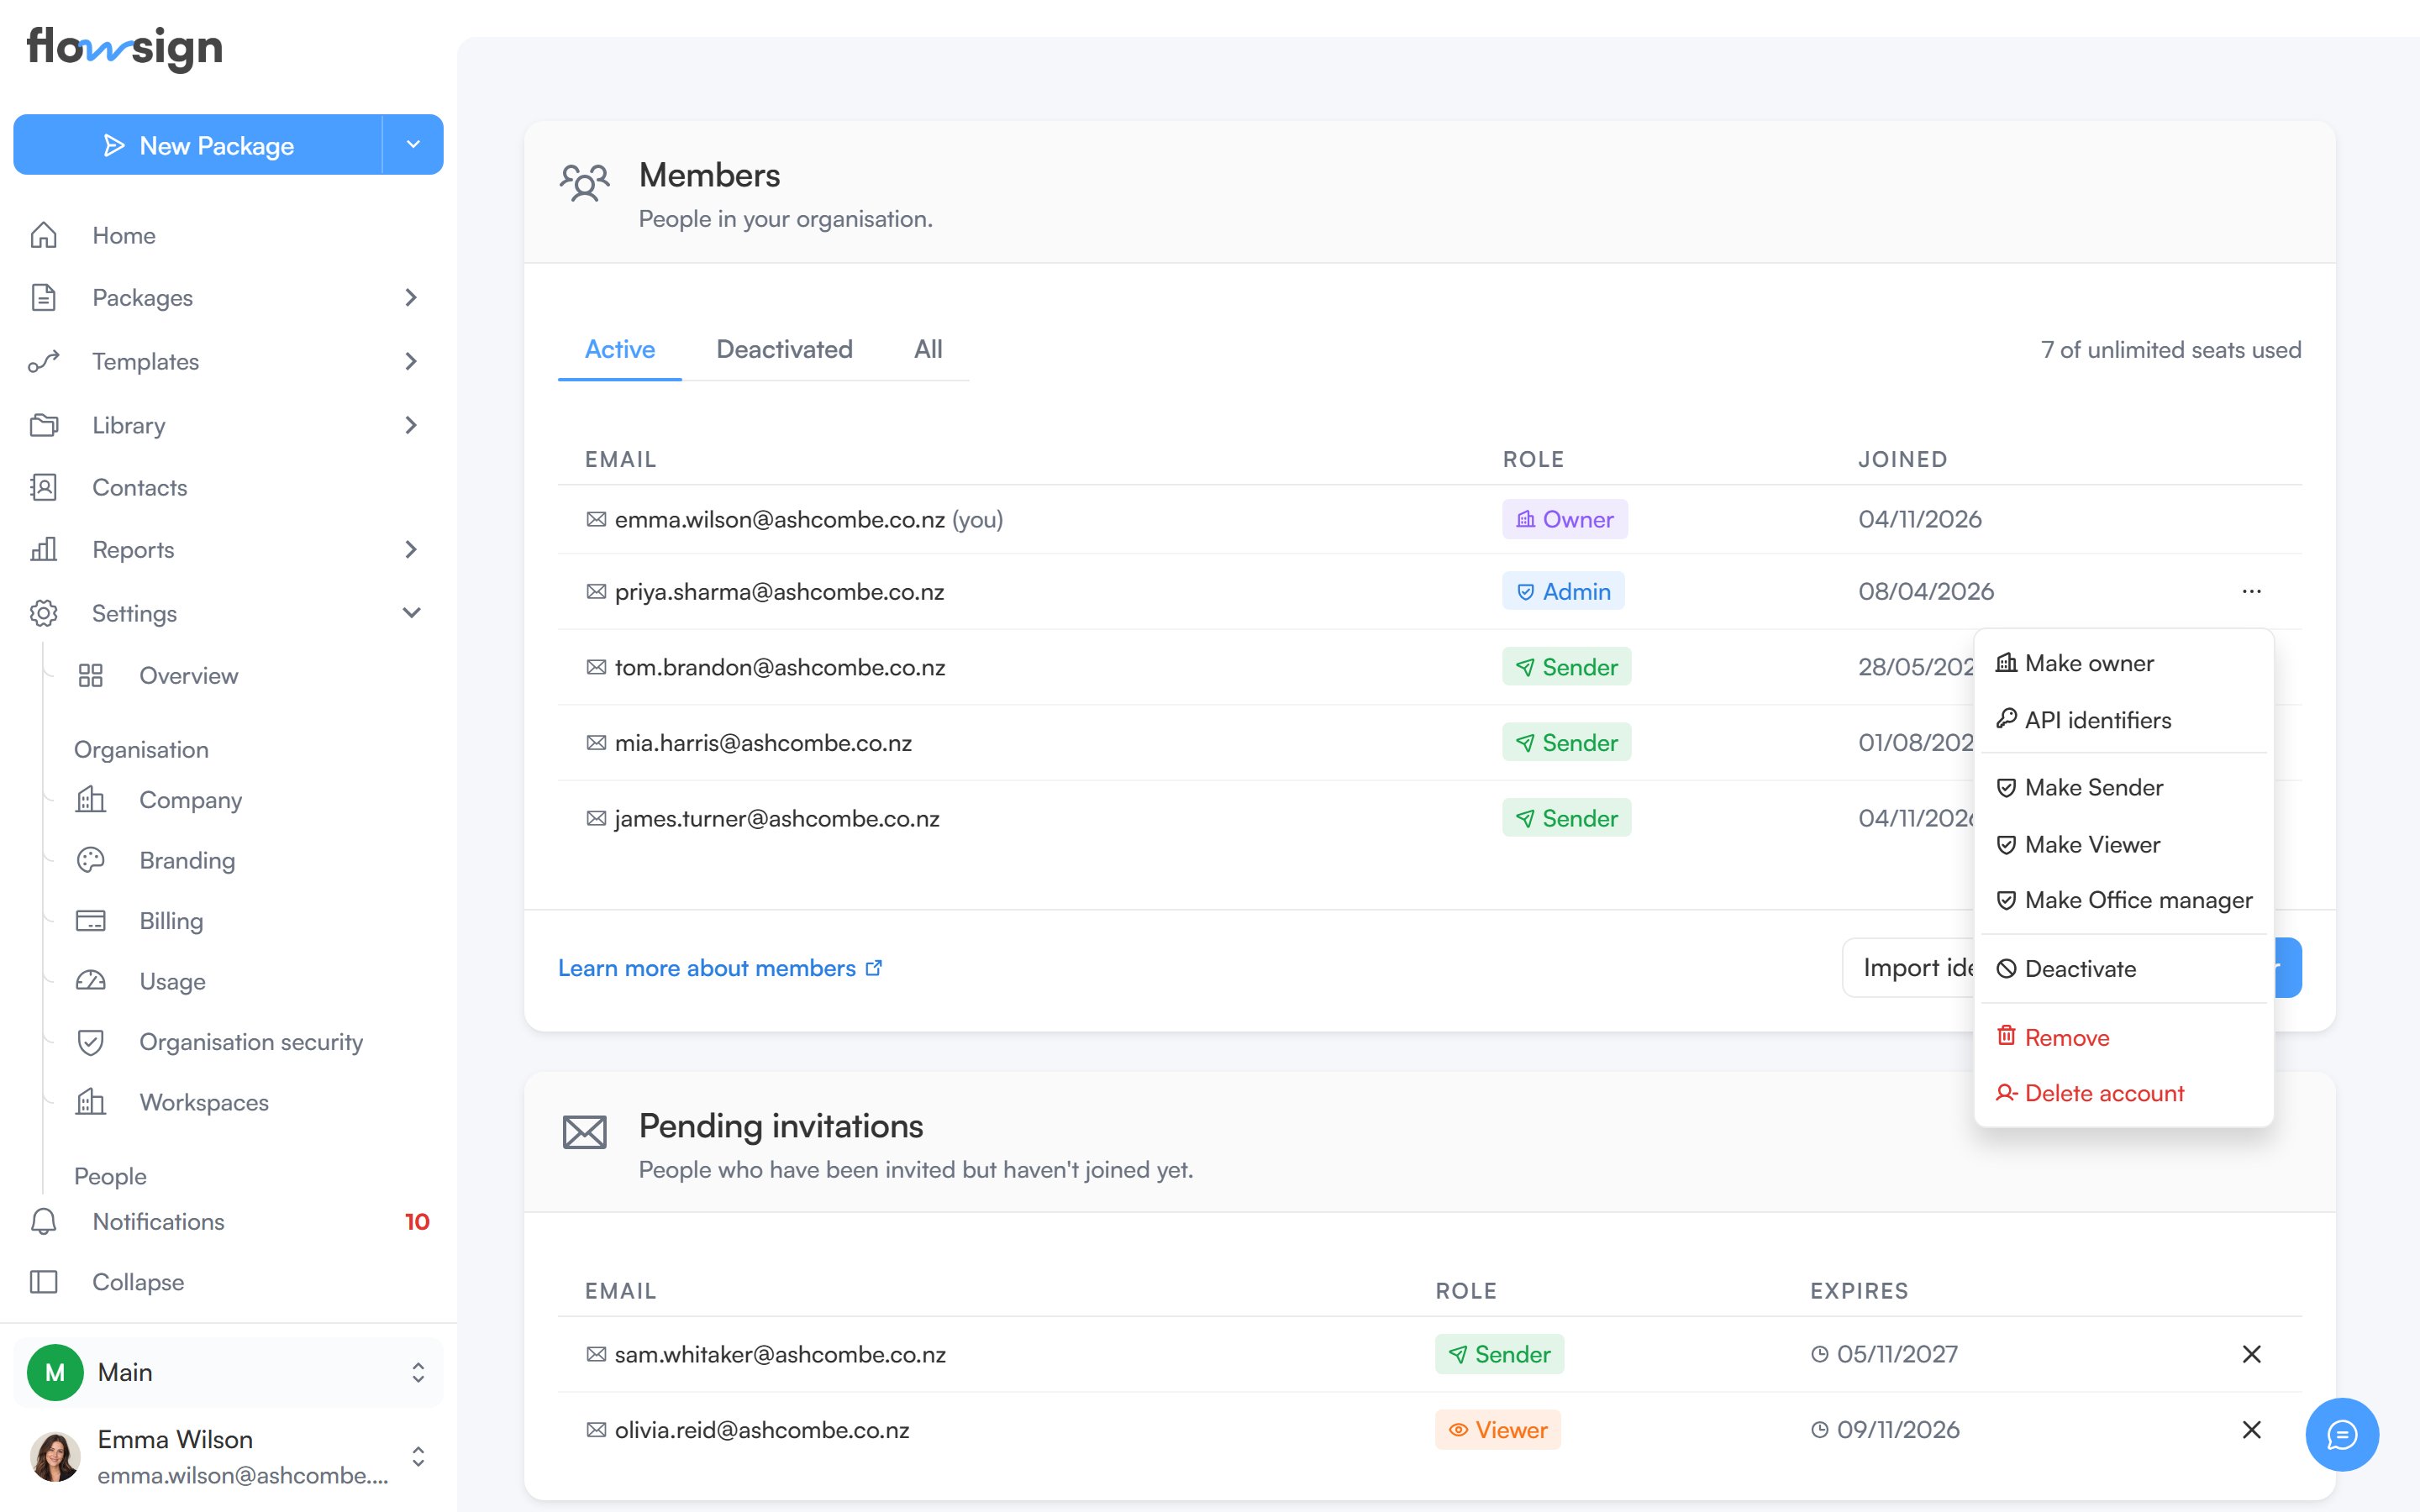
A member's actions menu.
- Members with permission to manage members can switch a non-Owner to another profile (Make followed by the profile name) or Remove them, but can’t change or remove someone with more access than their own. Remove takes someone out of the current workspace when they belong to another one. If it is their only workspace, it deletes their account, which only an Owner can do.
- An Owner can also Make owner or Revoke owner, set API identifiers, Deactivate or Reactivate a member, and Delete account. These stay with Owners and can’t be given to a custom role.
Owner
Owner is a built-in role that sits above every workspace. An Owner can do everything in every workspace, plus organisation-wide tasks such as security and ownership. A custom role can be given some owner powers, such as inviting members or billing, but security and ownership stay with Owners. While someone is an Owner, their workspace role has no effect. See the Owner role for the full list.Make or revoke Owner
Only an existing Owner can make someone an Owner or revoke it. Open the member’s actions menu and choose Make owner or Revoke owner, then confirm. Every change is recorded in the audit log. Someone whose Owner is revoked keeps their workspace role.If every Owner has left
If nobody in your organisation is an Owner any more, contact Flowsign support to recover access.Delete a member’s account
Only an Owner can delete another member’s account. Open the member’s actions menu and choose Delete account. If they own packages, choose an active member to take them over. Type their email address to confirm. Deactivate works the same way for their in-flight packages, and a deactivated member can be reactivated later. If the person hosts in-person signings, the dialog lists them under In-person hosting and asks you to choose a new host before they go. When there is more than one, Give all to hands every signing to one person, or you can choose a host per item. Remove and Deactivate ask the same. Their profile and sign-in methods go straight away, and they are signed out everywhere. Their audit history stays in anonymised form, and the deletion itself is recorded with who was deleted and who received their packages. You can’t delete your own account here, or the last active Owner.API identifiers
An API key that acts for members names the member each call is for. Identifiers are the values another system knows a member by, stored as a key and a value, for exampleemployee_id and RW-4821. Only an Owner can set them.
Open the member’s actions menu and choose API identifiers. A member’s email always matches, as does their scim_external_id when your identity provider set one, so neither can be set here. employee_id is offered first; Add identifier adds another. Keys are saved in lowercase: a key starts with a letter and holds up to 64 lowercase letters, digits, dots, dashes or underscores. Keys are not case sensitive when a call names a member, and email values ignore letter case, but every other value must match exactly. A member holds one value per key, and no two members in your organisation can share the same key and value.
Import identifiers, below the table, sets them in bulk from a CSV whose first column is email and whose other columns are identifier keys, such as employee_id. Empty cells leave a value as it is, and rows that can’t be applied are listed with the reason.